All services

Security & QA testing

We test applications the way an attacker and a demanding user would. Static analysis and dependency scans run against the source code, dynamic scanners and AI-assisted penetration tests probe the running application, and load tests show where it slows down. The same workflow powers Hoplite, our in-house security product.
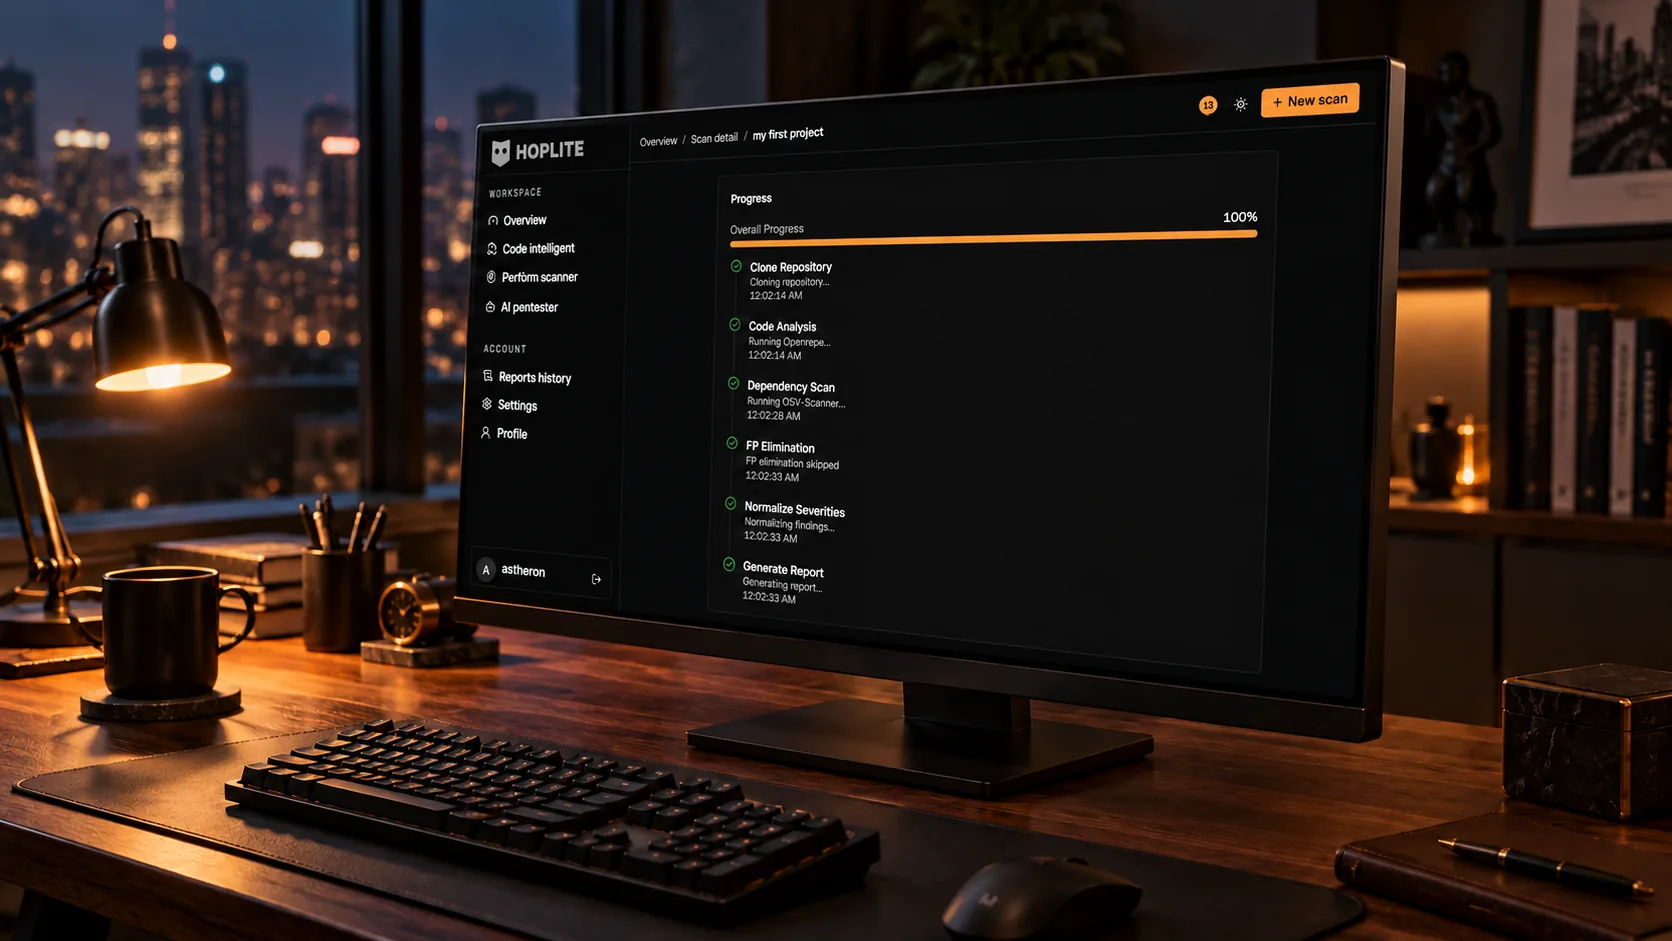
Hoplite security scan completing code analysis and dependency checks
Hoplite · AI-powered web security

What it's for

  1. 01Security review before a launch or major release
  2. 02Recurring scans for applications in production
  3. 03Load testing ahead of an event or campaign
  4. 04QA for web and mobile releases

What we deliver

  • Penetration Testing (manual and AI-assisted)
  • Static Code Analysis
  • Dependency Vulnerability Scanning
  • Load & Performance Testing
  • Functional QA & Test Plans
  • Findings Reports with Remediation Steps

How we approach it

Findings are grouped by severity, each with the evidence and a clear fix, so your team knows what to address first.

Our five-stage process

Tell us what you’re building.

Share the challenge and where you’re stuck. We reply within 24 hours and help you figure out the next step.